Audit Evidence Has to Be Rebuilt Every Time
Without a structured audit trail built as work happens, every review starts from scratch: logs pulled from multiple tools, timelines reconciled from memory.
For Cybersecurity & Compliance Teams
Tolmete gives cybersecurity and compliance teams one platform to log security work, track effort across incidents and initiatives, and turn it into structured evidence for audits, regulatory reviews, and post-mortems. Tolmete creates structured records as work is logged, timestamped, and attributed from the start.
The Problem
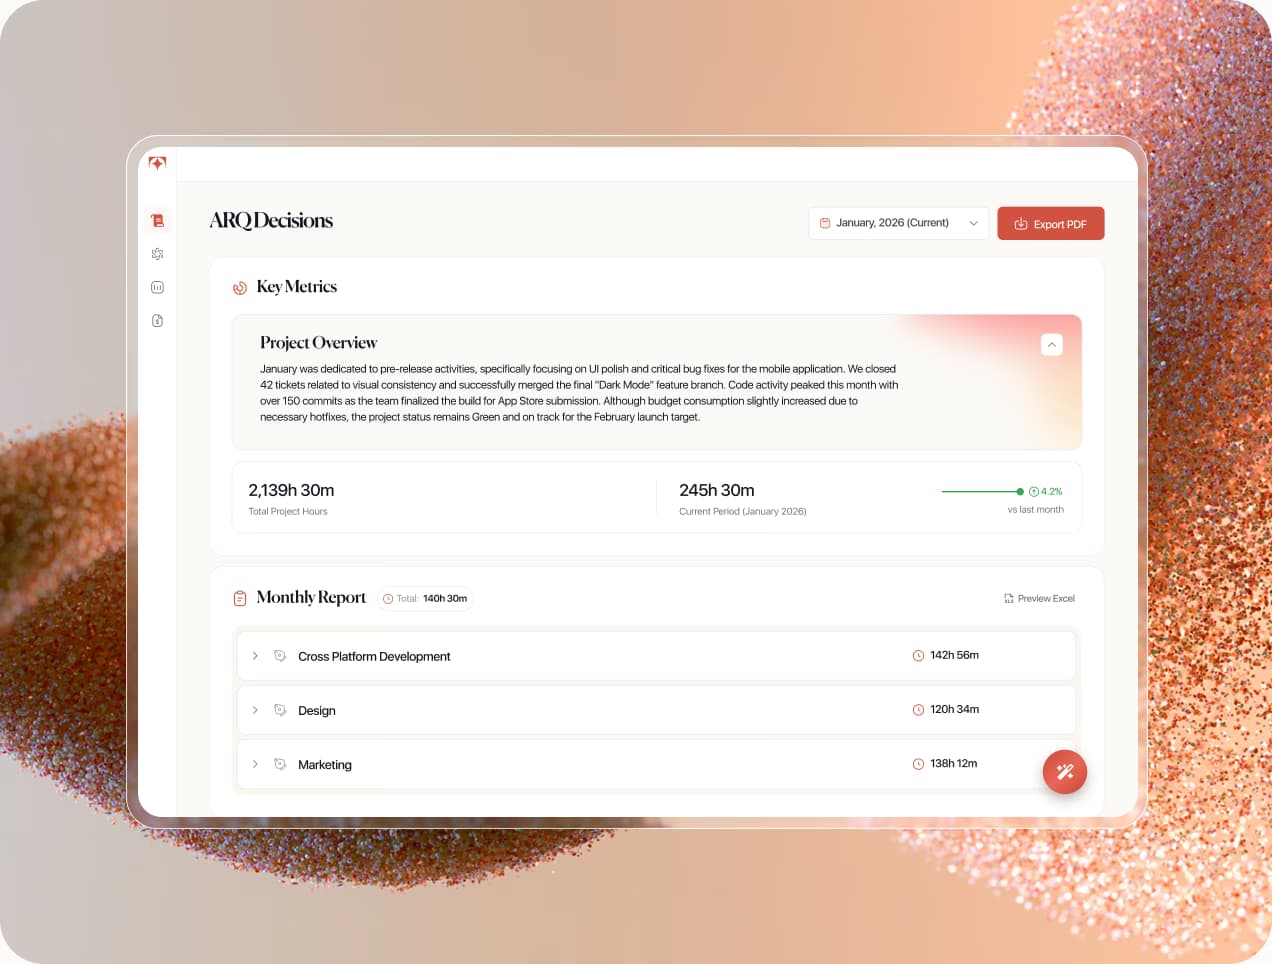
Cybersecurity and compliance teams work under constant scrutiny: audits, regulatory reviews, incident post-mortems, and board-level reporting. When evidence is needed, most teams rebuild the timeline from tickets, inboxes, and memory — documentation that was never designed to withstand review.
Tolmete builds that record as work progresses, giving security teams structured evidence for audits, regulatory reviews, and post-mortems without requiring reconstruction.
Without a structured audit trail built as work happens, every review starts from scratch: logs pulled from multiple tools, timelines reconciled from memory.
Triage, investigation, and remediation effort gets handled but rarely logged with enough context to support a post-mortem, an effort review, or leadership reporting.
Tracking who worked on which control, for how long, and under which framework takes time that adds no security value. Compliance reporting should come from work already logged.
Stalled security initiatives, unassigned remediation ownership, and SLA breaches are hard to see across tools. By the time coverage gaps surface, the window to act has already closed.
Position
Most security teams run delivery in one tool, incident tracking in another, and compliance documentation in a third. By the time an audit arrives, evidence exists in fragments across all of them.
Incidents triaged, patches deployed, compliance controls validated, initiatives delivered.
Contributor, Activity Type, compliance framework, timestamp, initiative context.
Stalled tasks, coverage gaps, SLA exposure, effort without supporting activity.
Risk summary, recommended action, evidence already attached.
Timestamped activity records organized by project, initiative, and framework before anyone asks.
Core Value
Security and compliance teams carry more documentation pressure than most: every incident needs a timeline, every control needs evidence, every audit needs a structured record. Tolmete gives teams the tools to build that record as work happens, not after someone asks for it.
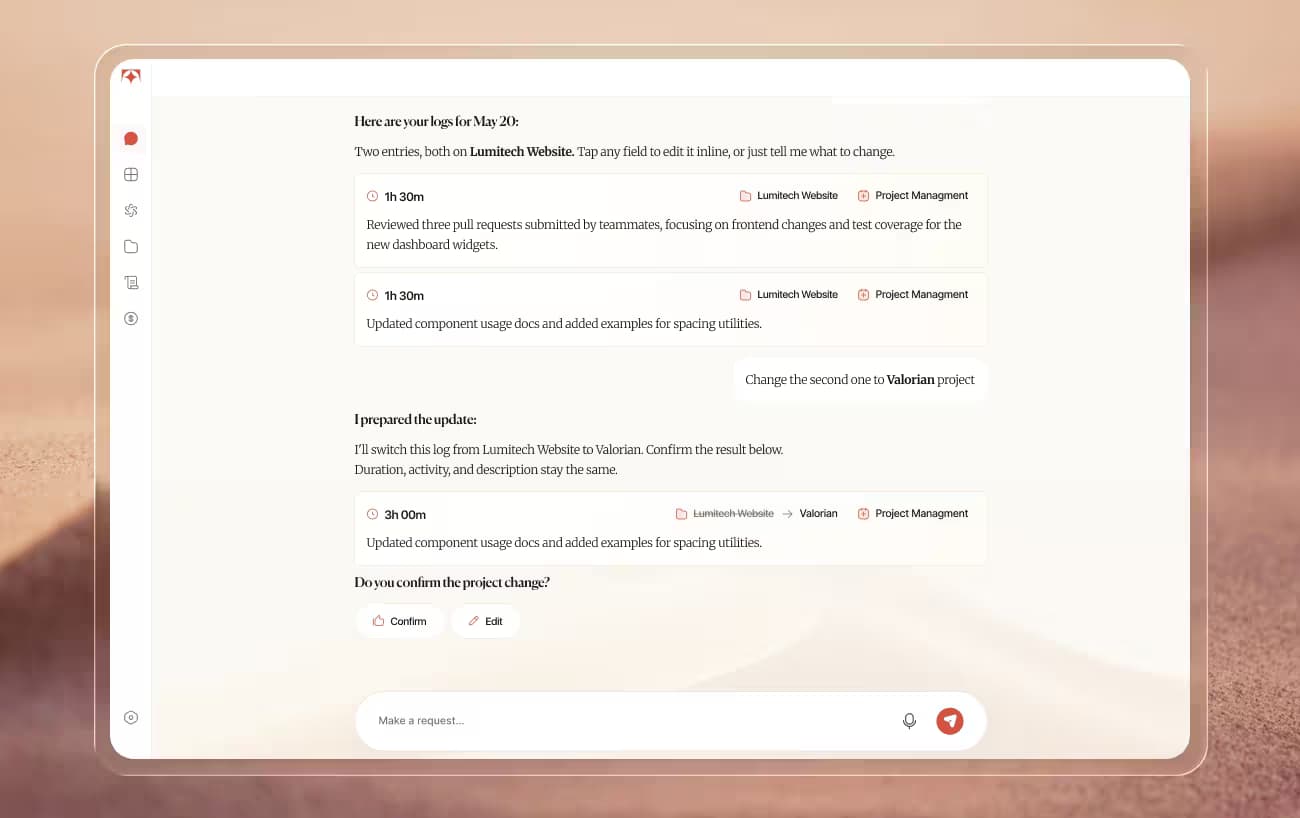
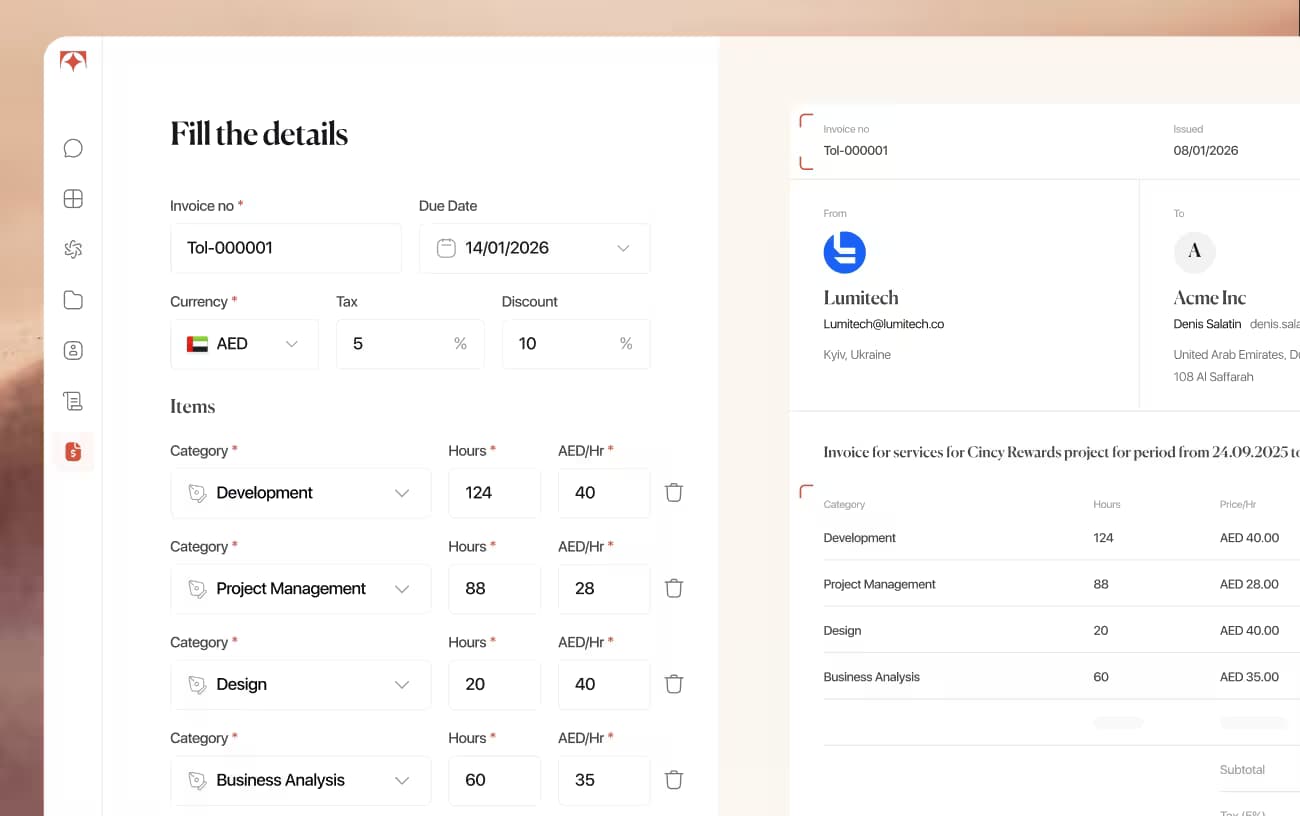
Security engineers and analysts describe completed work in plain language by text or voice, and Tolmete prepares a structured time log draft. The contributor reviews and confirms it before saving.
The impact:
Cleaner records of security work tracking across incidents, vulnerability management, and compliance tasks, with less admin.
Tolmete shows managers how security projects and compliance tasks are progressing using real activity signals, not just manual status updates.
The impact:
Teams see where work is moving, where it is stalling, and where a delivery gap may grow into an audit finding or missed SLA.
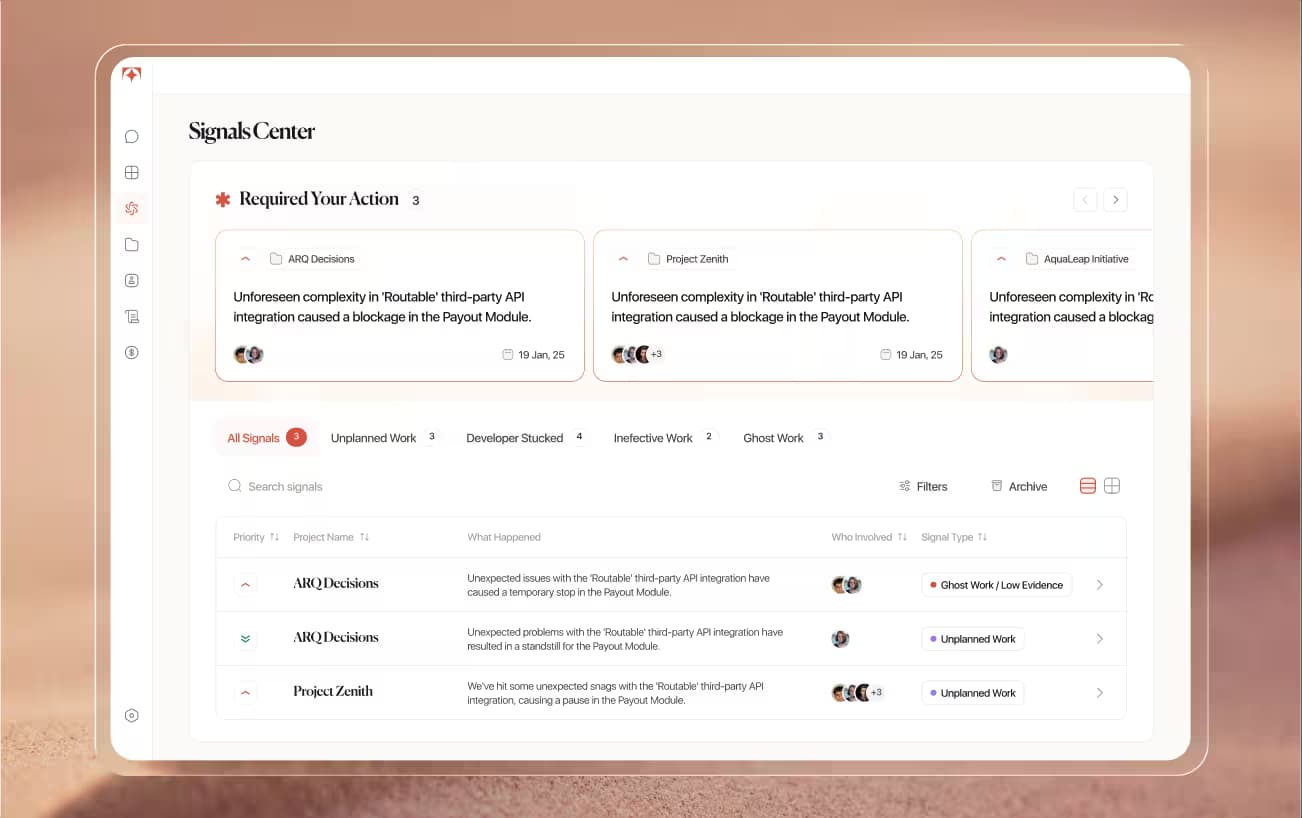
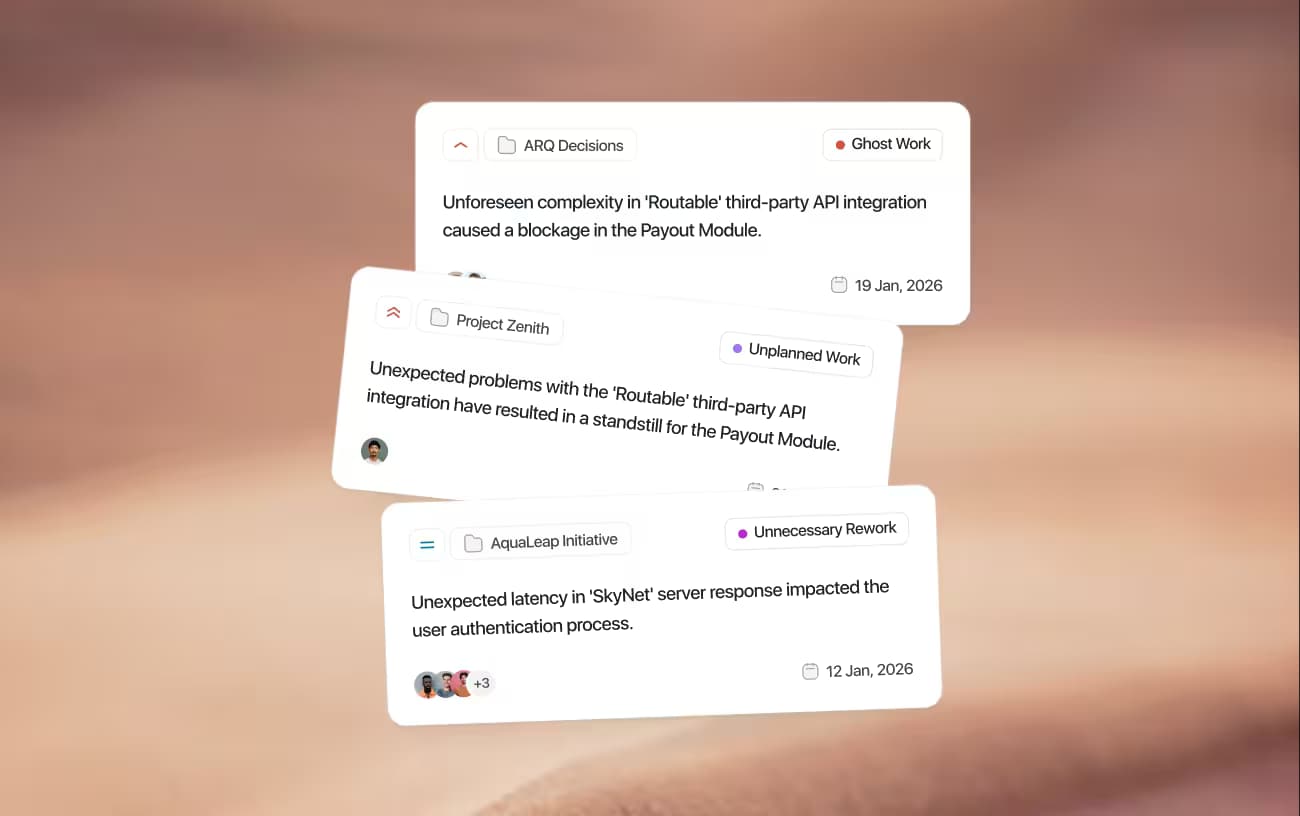
Tolmete surfaces patterns like stalled vulnerability tasks, unassigned work, growing SLA exposure, or initiatives with no recent progress, each with a recommended next step.
The impact:
Teams respond while a gap is still manageable, before it becomes a finding, an escalation, or a post-mortem issue.
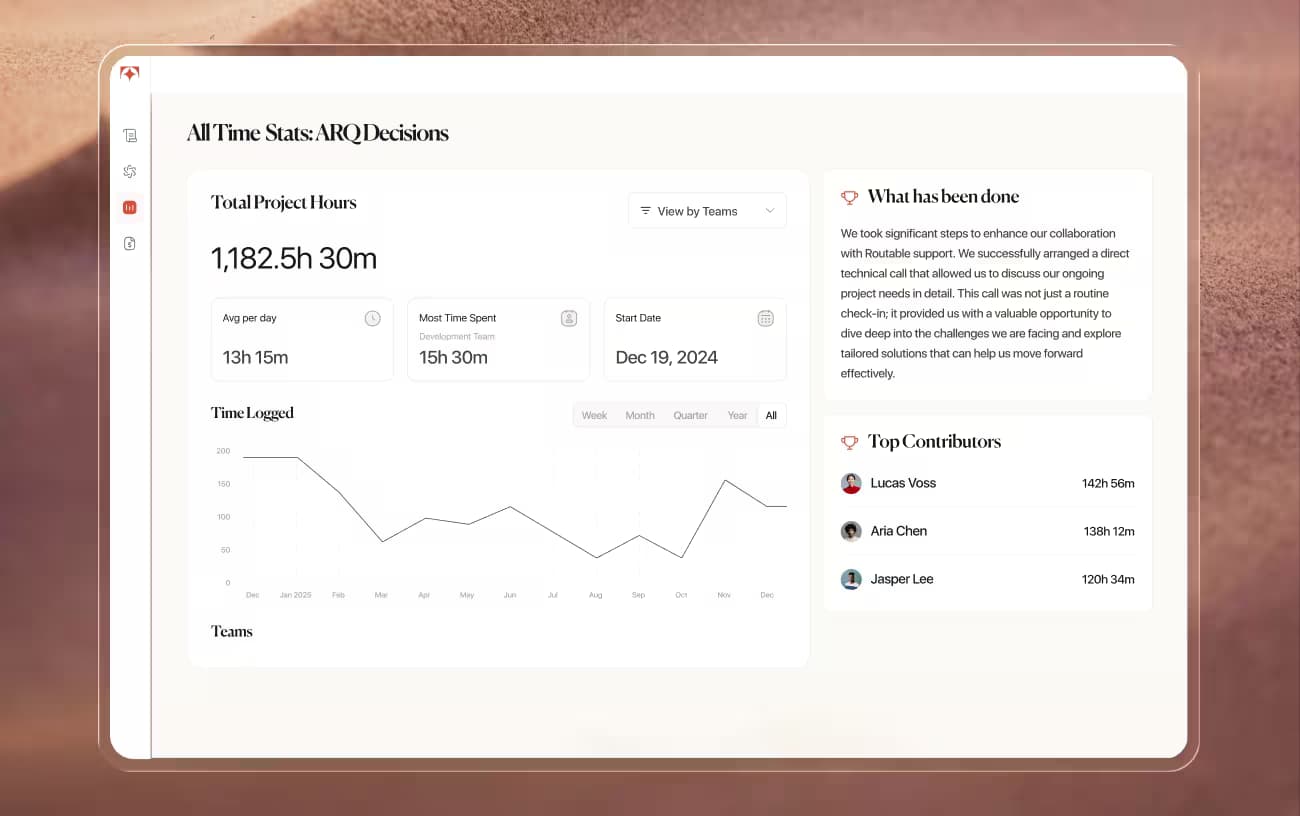
Tolmete links logged security work to delivery activity and structures it into timestamped activity records that hold up under audit, board reviews, and incident post-mortems.
The impact:
Audit prep no longer relies on someone to reconstruct the timeline from tickets and memory. The evidence is organized as the work happens.
When billing closes, Tolmete organizes approved logs by client, project, period, and Activity Type, keeping T&M, retainers, and fixed-fee work separate. Invoice inside Tolmete or push to Zoho Books or QuickBooks.
The impact:
Security effort becomes easier to explain in leadership reporting, with a clear record of what was delivered and where capacity was spent.
Audit windows don’t wait. Tolmete keeps AI delivery intelligence and audit records connected across incidents, vulnerability tasks, and compliance projects, so security teams walk into every review with evidence already organized
Log Work
Detect Delivery Risk
Review Initiative Health
Build Audit Evidence
Report Effort to Leadership
How It Works
Tolmete consolidates security work, incident activity, and compliance tasks into a single structured record upon delivery
01/05
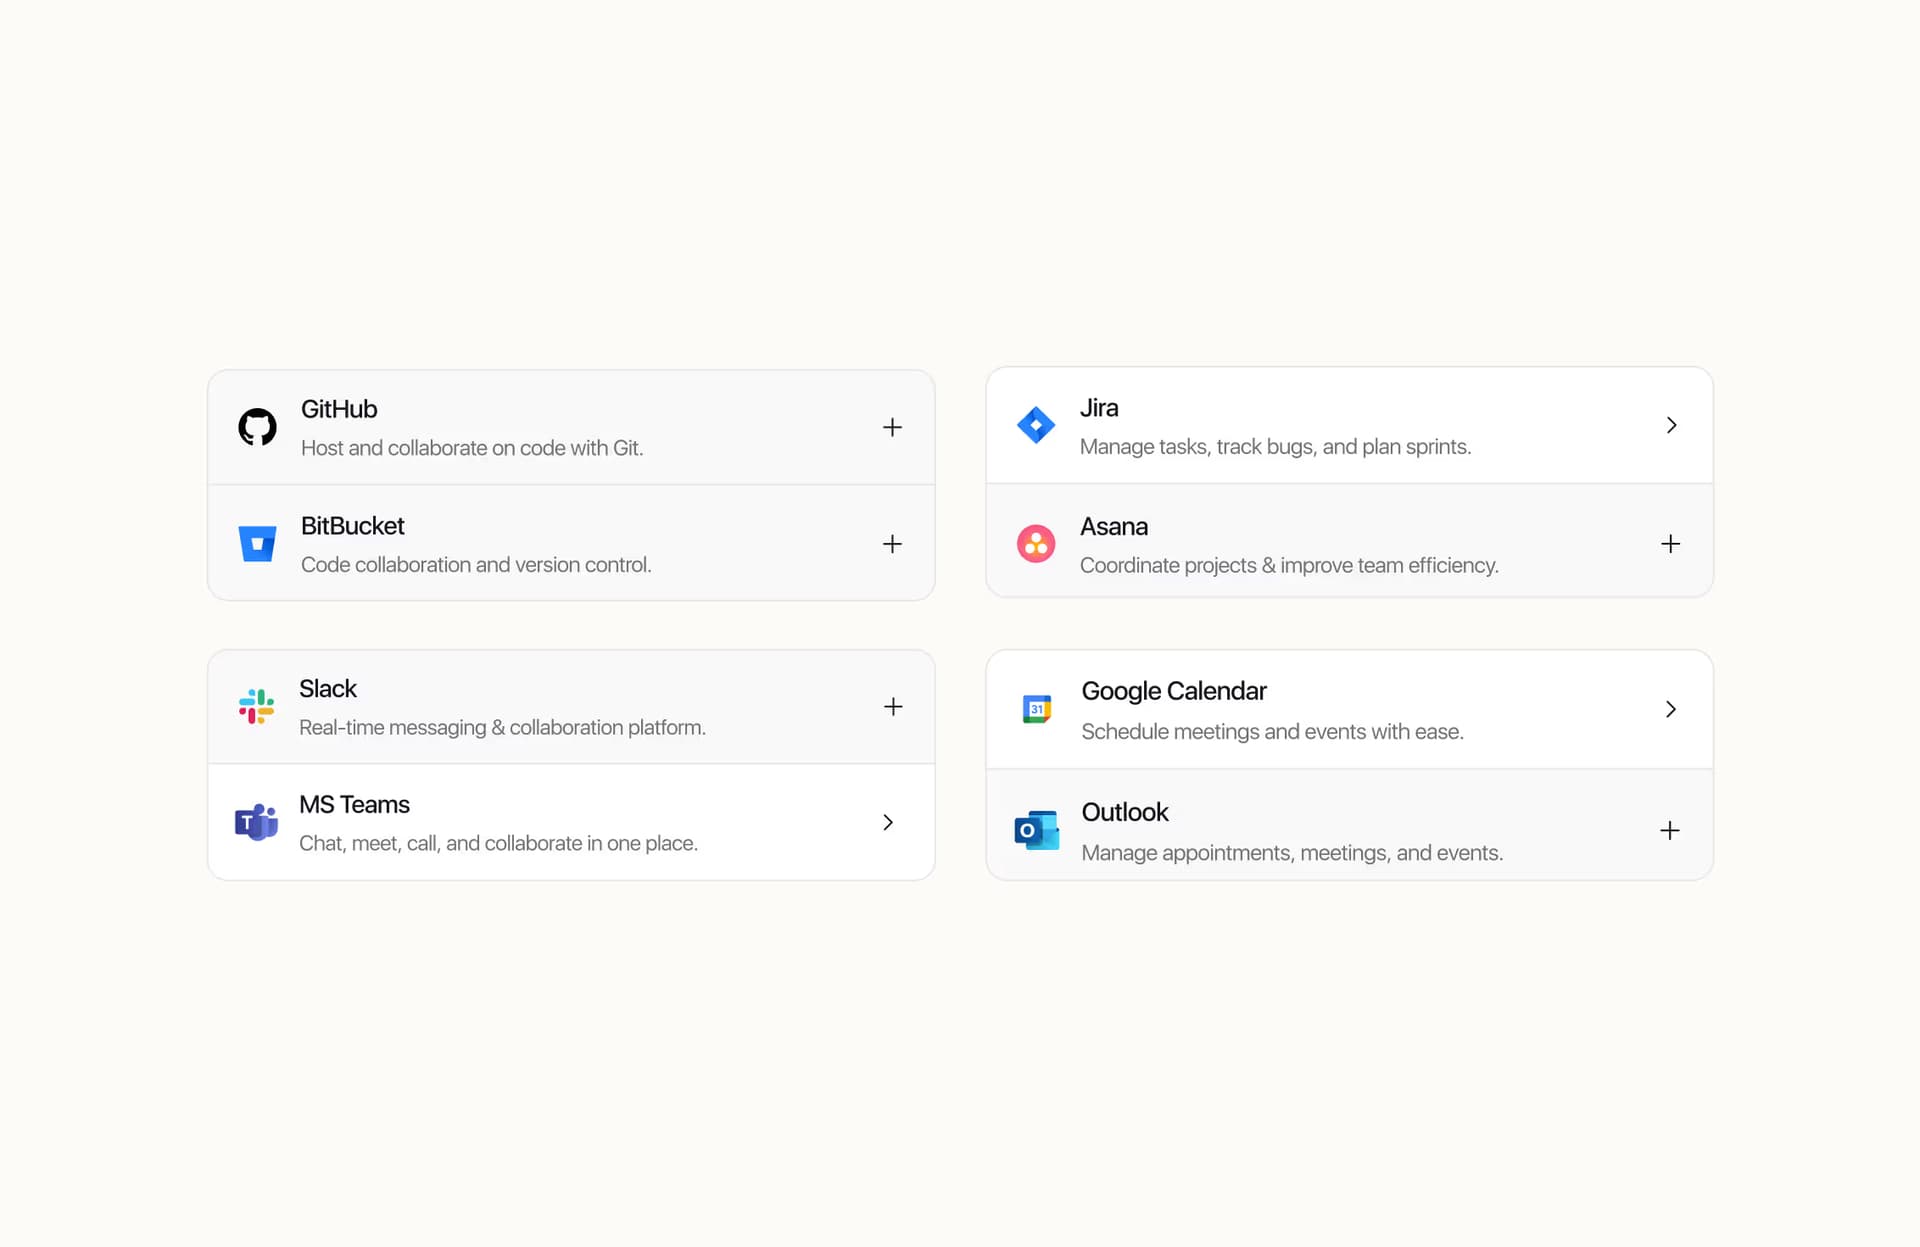
Tolmete integrates with your workflow, ticketing, and project tools, reading selected metadata and ticket audit trails. It never connects to raw security telemetry: SIEM event logs, EDR telemetry, vulnerability scan data, client infrastructure, or credentials. You can start with AI-assisted time logging and add integrations later.
Use Cases
The moments that cost security teams the most aren’t random. They’re the audit that arrived without organized evidence, the incident timeline nobody logged, the vulnerability that sat open too long. Tolmete gives teams the visibility to handle each of them.
Walk into an audit with evidence already organized, not assembled the week before.
Instead of: Reconstructing activity from ticket exports, inboxes, and engineer recall.
With Tolmete:
Compliance leads have timestamped records organized by project, initiative, and framework, ready for structured audit reviews and post-mortems without manual preparation.
Understand what the incident cost without asking everyone to remember.
Instead of: Piecing together a timeline from three tools and five engineers after the fact.
With Tolmete:
Incident response reporting is already structured by activity, contributor, and time — ready for post-mortems, insurance questions, and leadership briefings.
Know which vulnerabilities are behind schedule before the audit window opens.
Instead of: A critical vulnerability remediation task sitting open for six days because no single view showed the full queue.
With Tolmete:
Security managers see which tasks are behind, where SLA exposure is growing, and which controls need attention — with supporting audit evidence already.
See where security work is moving and where it is not before the next leadership meeting.
Instead of: Asking team leads to summarize progress across incidents, projects, and vulnerability queues by hand.
With Tolmete:
Security managers get one view of initiative health, open risks, and evidence-based reporting ready to share with leadership.
For many security teams, audit preparation consumes a significant share of capacity that adds no security value: time spent reconstructing evidence that should have been captured while the work was being logged. Estimate how much your team loses to reconstruction work before every audit.
Try the ROI CalculatorTeams and Features
Security organizations run on accountability: CISOs answer to boards and regulators, compliance leads manage framework deadlines, operations teams track vulnerability queues, and engineers respond to incidents at any hour. Tolmete gives each role structured visibility without adding process overhead.
Get a clear picture of where security efforts are headed, which initiatives are at risk, and what evidence exists to support board reporting, regulatory reviews, and audit conversations.
AI Delivery Intelligence, Intelligent Risk Alerting, Evidence-Based Signals
Track progress across security projects, compliance frameworks, and vulnerability programs. See which controls need attention and where gaps may affect compliance reporting deadlines.
AI Delivery Intelligence, Evidence-Based Signals, Intelligent Risk Alerting, AI Mitigation Plans
Track the distribution of effort and resolution time across incident queues. Identify bottlenecks and analyst burnout risks before they slow response times or jeopardize SLA commitments
AI Time Logging, AI Delivery Intelligence, Deep Integrations
Log incident work, investigation hours, and remediation effort by text or voice, without filling out timesheets after the fact or reconstructing what happened three days later.
AI Time Logging, Deep Integrations, Voice Time Tracking
Why Tolmete is Different
Ticketing tools, project boards, and communication channels each capture a piece of security work. What auditors, boards, and post-mortems ask for is a single structured record that connects it all, and that record rarely exists until someone has to build it under a deadline
The Old Way
The Automated Way
Separate tools can confirm that a project shipped. Tolmete serves as project margin tracking software for agencies, helping teams see whether the project remains profitable, where effort has expanded, and which approved work is ready to support billing
Privacy and Trust
Security teams work with some of the most sensitive data in any organization. Tolmete does not inspect source code, raw security telemetry, credentials, private messages, or client infrastructure. It reads only the metadata and patterns around how security work moves.
Tolmete adds structured records using only activity metadata. It never connects to SIEM platforms, EDR tools, vulnerability scanners, or production infrastructure.
Tolmete reads the metadata and patterns, never the raw security content. Incident investigations, threat intelligence, and client environments stay outside the platform.
AI-prepared time logs are reviewed and confirmed by the person who did the work. Security engineers control exactly what gets recorded.
Tolmete processes activity logs within a secure, isolated environment. Your data is never used to train public LLMs or retained for AI training.
Audits, post-mortems, and board reviews all ask the same question: can you prove what your team did? Tolmete gives cybersecurity and compliance teams one platform where security work tracking, compliance reporting, and audit-supporting records stay connected from the first log to the final review.
FAQ
Everything you need to know about Tolmete.